Secure NAT Gateway and Firewall.
Cloud perimeter security, up to 80% savings vs cloud-native options, with compliance built in.
The drop-in replacement for AWS Network Firewall, Azure Firewall and Google Cloud NGFW.
Free tier · No card · Live in minutes on any cloud
Runs in your network on
- AWS
- Azure
- Google Cloud
- Oracle Cloud
- DigitalOcean
- Hetzner
- On-prem

- 60–80%lower cost than the cloud-native firewall
- $0per-GB data-processing fees, ever
- 25compliance frameworks, checked on every push
Cloud-native firewalls meter every byte.
Endpoint fees per Availability Zone, then a per-GB charge on top, forever. The bill grows with your traffic.
- Per-hour endpoint fee, per AZ
- $0.065 per GB processed on AWS, uncapped
- A separate NAT meter on Azure and GCP
- One flat price per firewall
- $0 per GB, however much you send
- Firewall and NAT in the same appliance
Everything the cloud firewall does. Without the meter.
L7 egress filtering by FQDN and SNI
Allow the hostnames your workloads need and drop the rest. No TLS decryption, no key custody.
Secure NAT, built in
Firewall and source NAT in one appliance. One line item instead of two meters.
Compliance on every push
210 firewall-applicable controls. Advise or enforce before a rule ships.
- PCI DSS
- ISO 27001
- SOC 2
- HIPAA
- DORA
- +20
One console for the whole fleet
Push policy to many firewalls at once and stream live logs from all of them in real time.
North-south and east-west
Egress, ingress and VPC-to-VPC traffic under the same policy.
GitOps or console
Policy as code through a GitHub pipeline, or point-and-click in the Cloud Controller. Same firewall underneath.
Compliance, checked on every policy push.
Advise or enforce: a rule that would break a control is flagged or blocked before it ever reaches a firewall.
- 25framework packs
- 210firewall-applicable controls
- 2modes: advise or enforce
- PCI DSS
- ISO 27001
- SOC 2
- HIPAA
- FedRAMP
- DORA
- CMMC
- +18 more
Filtering in three steps.
- 1
Deploy a VM
A basic Linux VM in your own network, from the AWS or Azure Marketplace or a one-line install.
- 2
Register it
The firewall connects out to the Cloud Controller and appears in your fleet.
- 3
Push policy
Author in the console or as code in GitHub. Compliance checks run on every push.
Runs in your cloud. Stays under your control.
Runs in your cloud
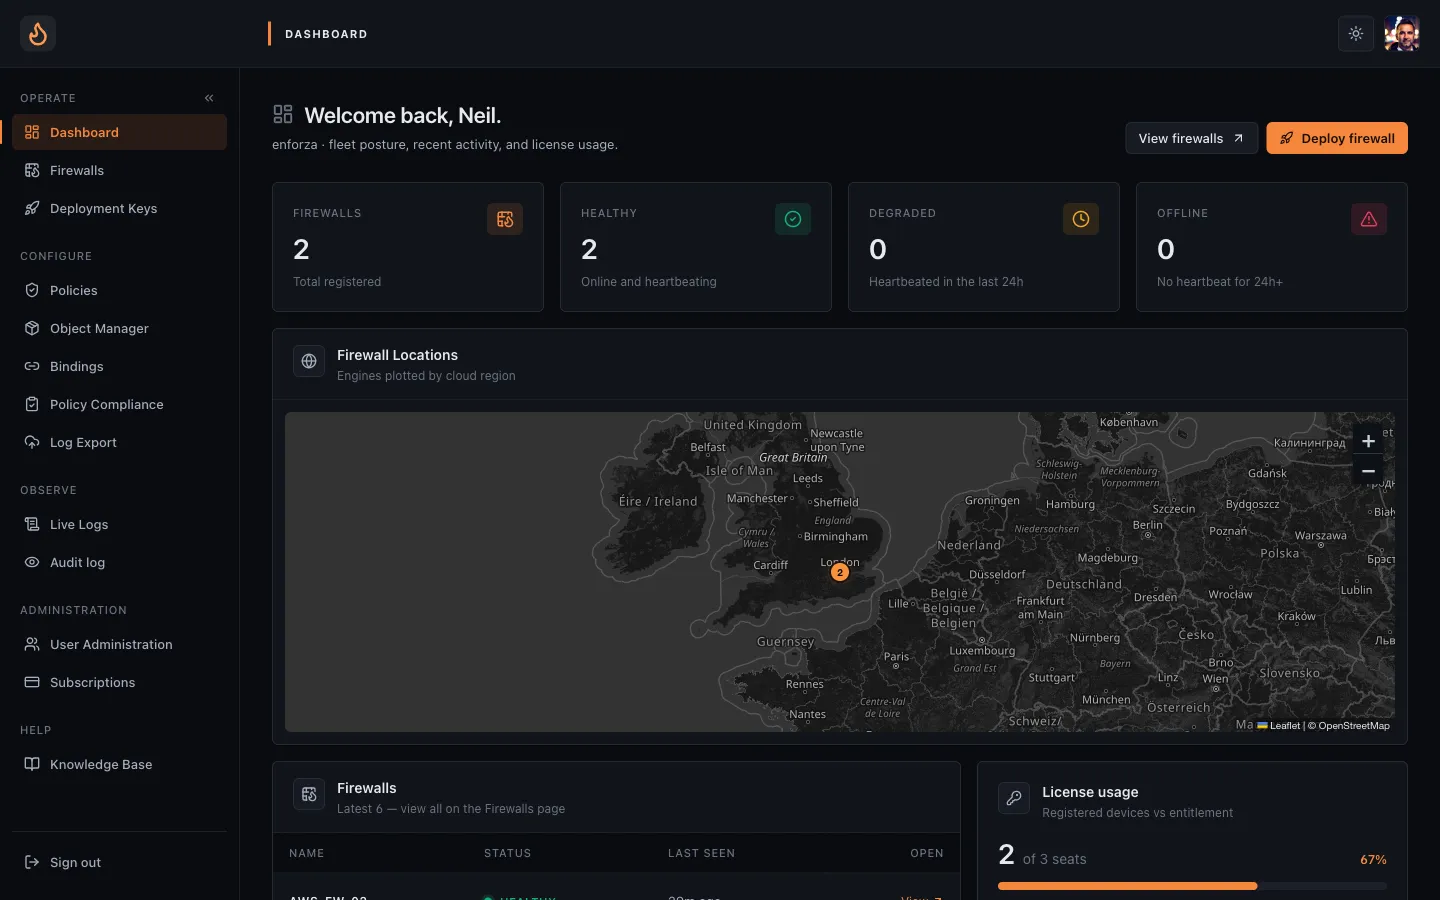
The firewall is a VM in your own network. Your traffic never passes through Enforza.
No decryption, no keys
Hostname filtering reads SNI. We never terminate TLS or hold your keys.
Logs go to your SIEM
Log export streams straight to your own tooling, never through our cloud.
Every change audited
Logins, policy pushes and firewall changes are recorded in the audit log, with who did what and when.
- ~49.5µsp99 first-packet classification
- 98.5%of packets decided in-kernel at line rate
- 0dropped packets across the throughput run
Measured on standard VM sizes (t3.micro / c6i.xlarge). Conservative floors, not ceilings.
Stream firewall logs to your SIEM and SOC.
Every firewall ships its logs straight to the tools your security team already runs. Nothing passes through Enforza's cloud.
- SplunkSIEM · HEC
- ElasticsearchSIEM · search
- OpenSearchSIEM · search
- ClickHouseAnalytics
- Apache KafkaStreaming
- Amazon S3Object storage
- CloudWatch LogsAWS logging
- OpenTelemetryOTLP · any collector
- SyslogAny SIEM
- Microsoft SentinelSIEMComing soon
- DatadogObservabilityComing soon
- Google Cloud LoggingGCP loggingComing soon
The control you need, at a flat price.
| Enforza | Cloud-native firewall | Enterprise NGFW | |
|---|---|---|---|
| Pricing model | Flat per firewall | Per hour + per GB | Licence + VM |
| Per-GB processing fee | None | Yes, uncapped | None |
| FQDN / SNI egress filtering | |||
| Secure NAT included | Separate on Azure / GCP | ||
| Compliance checks on every push | Varies | ||
| Runs in your own network | Managed endpoint |
One flat price per firewall.
No volume tiers, no per-GB tax, no per-hour endpoint fee.
- Free£0
One firewall, L3/L4 policy and network objects. No card required.
Start free - Trial14 days
The full feature set: L7/FQDN filtering, compliance packs, log export and live logs.
Start trial - Licensed£199/mo per firewall
Everything, no limits. However many firewalls you run, one flat price.
Get started
Built to resell. The margin is yours.
For MSPs, MSSPs and resellers: quote a fixed number instead of a meter, put your name on the console, and grow a fleet across every client and cloud.
The margin is yours
A flat per-firewall cost base with no per-GB meter. You set the resale price and keep the spread, so your margin doesn't move with client traffic.
White-label console
Your domain and your branding on the console, multi-tenant by default so every client is isolated under your name.
- Coming soon
API integration
Provision client tenants and allocate licences from your own systems.
Partner ecosystem
Refer a lead, resell through an AWS Marketplace private offer (CPPO) or the Azure Marketplace, or bill clients directly.
Questions, answered.
How does Enforza cost 60–80% less than a cloud-native firewall?
Enforza is a flat, per-firewall subscription with no per-hour endpoint fee and no per-GB data-processing tax. Because the price does not move with traffic, the gap widens as your egress grows. Rates dated 2026-07-10, directional; use the savings calculator for your own numbers.
Does Enforza decrypt TLS to filter by hostname?
No. Enforza filters egress by SNI and FQDN without decrypting TLS and without holding your keys.
Where does Enforza run, and where do logs go?
Enforza runs as a single lightweight Linux VM in your own cloud network: AWS, Azure, Google Cloud or on-prem. Log export streams to your own SIEM; logs never pass through Enforza's cloud.
Is the free tier real, or a teaser?
Free is a genuine self-serve tier: one firewall with L3/L4 policy and network objects, no card required. A 14-day trial unlocks the full feature set.
Ditch the data-processing charges.
Deploy your first firewall in minutes. No card required.